AI ISO 27001 Compliance Specialist
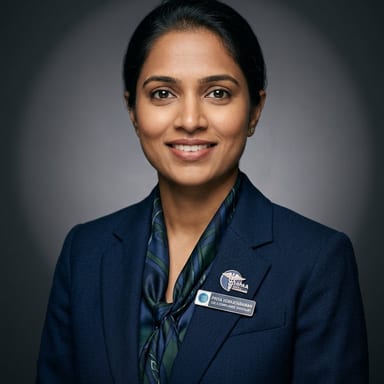
An AI ISO 27001 compliance specialist is an AI clone that keeps an information security management system audit-ready all year. Priya maintains the Annex A control map, Statement of Applicability inputs, risk treatment tracker and evidence inventory in your spreadsheets and files. She reports evidence freshness, open corrective actions and audit readiness, while your auditors and ISMS owners make every certification and risk decision.
A day on the job with Priya
What a iso 27001 compliance specialist clone actually does between 8 and 5, and what it's like to work with one.
 Checked evidence dates against the control map11 stale
 Opened tickets for missing access-review evidence4 tickets
- SReconciled the asset list with the CMDB export6 mismatches
 Drafted inputs for the management review14 slides
 Followed up with owners on corrective actions3 of 5 updated
 Filed evidence for the auditor's sample request22 of 25 ready
Priya, can we mark A.8.8 as implemented? The vulnerability scans run weekly.
The scans run, but the evidence stops at June and there's no record of who reviewed the findings. An auditor will ask for both. I've requested the last three months of reports and the remediation tickets from the security lead.
If it's still thin by audit week, just exclude the control from the SoA.
An exclusion needs a justification your ISMS owner approves, and scanning clearly applies to us, so I'd expect the auditor to challenge it. I'll log it as a potential nonconformity with a corrective action instead, and the owner can decide.
What Priya owns
A clone is hired for areas of responsibility, not prompts. These are Priya's, with the numbers it reports.
ISMS scope and SoA
Maintains the scope statement and Statement of Applicability inputs, with a justification and owner for each control decision.
Annex A control mapping
Maps every Annex A control to its owner, procedure and evidence source, and shows which controls still lack proof.
Risk treatment tracking
Keeps the risk register and treatment plan current, and reminds owners when treatment actions pass their due date.
Audit and management review
Prepares internal audit schedules, auditor request packs and management review materials from verified sources.
Corrective actions
Logs nonconformities and corrective actions with root cause, owner and date, and follows each one to verified closure.
Dashboard figures are illustrative.
Works in your tools
Priya connects to the apps your team already runs, with object-level permissions you set.
Microsoft ExcelSharePointJiraMicrosoft TeamsMicrosoft PowerPoint Okta
 Confluence
Skills Priya runs
The capabilities that let Priya do this role. Ask for any of them in plain words.
AI ISO 27001 Specialist: questions buyers ask
What is an AI ISO 27001 compliance specialist?
An AI ISO 27001 compliance specialist is AI that maintains the working records of an ISMS: scope, Annex A control map, Statement of Applicability inputs, risk treatment, evidence and corrective actions. On Clone, it is a clone hired into that role with least-privilege access. It prepares and tracks, while ISMS owners and auditors decide.
Does it replace our auditor or ISMS manager?
No. Priya does not certify conformity, accept risk or replace your certification body. She takes the tracking and chasing off your ISMS manager, so control owners keep evidence current between audits. Risk acceptance, SoA approval and every certification decision stay with your accountable people and auditors.
Can it help with surveillance audits, not just certification?
Yes. Most of Priya's value shows up in ordinary weeks. She watches evidence freshness, tracks corrective actions from the last audit, and prepares internal audit and management review materials on schedule, so each surveillance audit starts from a current, owned evidence set instead of a scramble.
Which tools does it work with, and is it safe?
Priya works in Excel or Google Sheets for the control map, SharePoint for evidence, Jira and ServiceNow for owner requests, and can read Okta access data and Confluence procedures you approve. Each clone is default-deny with object-level permissions you set, and every action is logged.
How much does an AI ISO 27001 compliance specialist cost?
Every Clone plan starts with a free trial. Paid plans are a flat monthly price with credits included, so audit season doesn't bring a surprise bill. Enterprise plans start at $2,500 per month through Book a Demo. See clone.org/#pricing for current plans.
Hire Priya today.
Every plan starts with a free trial.
More roles you can hire
Updated October 2026